AI Risk AssessmentShadow-AI discoveryCloud PostureExploit ValidationCI/CDContinuous PlatformReportsIdentity & accessAgentic Trust & Protection Platform
AI Risk Assessment

Know every AI you run, and which risks are real.

One free, agentless scan finds every model, agent, MCP server and AI key across your code, cloud and websites. It ranks the toxic combinations an attacker could actually use, maps them to the OWASP Top 10 for LLM and Agentic applications, and hands your team the fix.

Start a free assessment How it works
Agentless · read-only · no card, no sales call
Toxic combination LLM06 · ASI excessive agency · 3 hops
A support agent nobody inventoried can read customer records and call the internet
Each piece looks harmless alone: a public chat endpoint, an agent role with read access to the customer database, an outbound HTTP tool. Together they are one prompt away from a data leak.
Exposedpublic chat endpoint
Over-privilegedagent role reads customer DB
Way outoutbound HTTP tool
Example finding — illustrative, not a customer's Fix: draft pull request
Free
The complete estate assessment — no card, no sales call
4 clouds
AWS, Azure, Google Cloud and Oracle — one click each, read-only
0 agents
to install. Nothing runs on your hosts to get the full picture
Minutes
from connect to your first ranked risk, not weeks of interviews
One assessment, every answer

From the first commit to the agent in production.

Most tools answer one of these questions. The assessment answers them all from the same graph, so a risk found in one place is understood everywhere it matters.

Security
Find what you don't know you have
Shadow AI, forgotten agents, model keys in repos, exposed endpoints and cloud misconfigurations, mapped into one graph of what connects to what.
Safety
Assess the AI itself
Prompt injection, data leakage and excessive agency, assessed against the OWASP Top 10 for LLM and Agentic applications. For your riskiest apps, exploit validation proves it with a working test.
Development
Ship fast without shipping risk
A traffic light on every pull request — green ships, amber warns, red stops — and the fix arrives as a draft pull request, not a ticket.
Agent identity
Every agent gets a name you can verify
The agents you decide to keep get a cryptographic identity on the open SPIFFE standard, so you can prove which agent did what, to anyone.
Agent enforcement · Preview
Your rules, your choice of response
Learns each agent's normal behaviour and shows what it would have held. Watch, or alert your own tools through signed webhooks, per agent. Blocking is in preview and turns on only after you've reviewed real traffic.
Compliance
Evidence your auditor can use
Findings mapped to NIST AI RMF, ISO 42001, the EU AI Act, SOC 2 and more — stated as evidence toward a control, never as a pass.
Why a graph, not a list

Risk lives in the combinations.

A list of findings tells you a hundred things might be wrong. The assessment walks the graph — code to cloud to agent — and ranks the few paths where an exposed entry, a way through and something worth reaching line up.

Agents add a new kind: one agent allowed to read two datasets that are harmless apart and sensitive together. We flag those too.
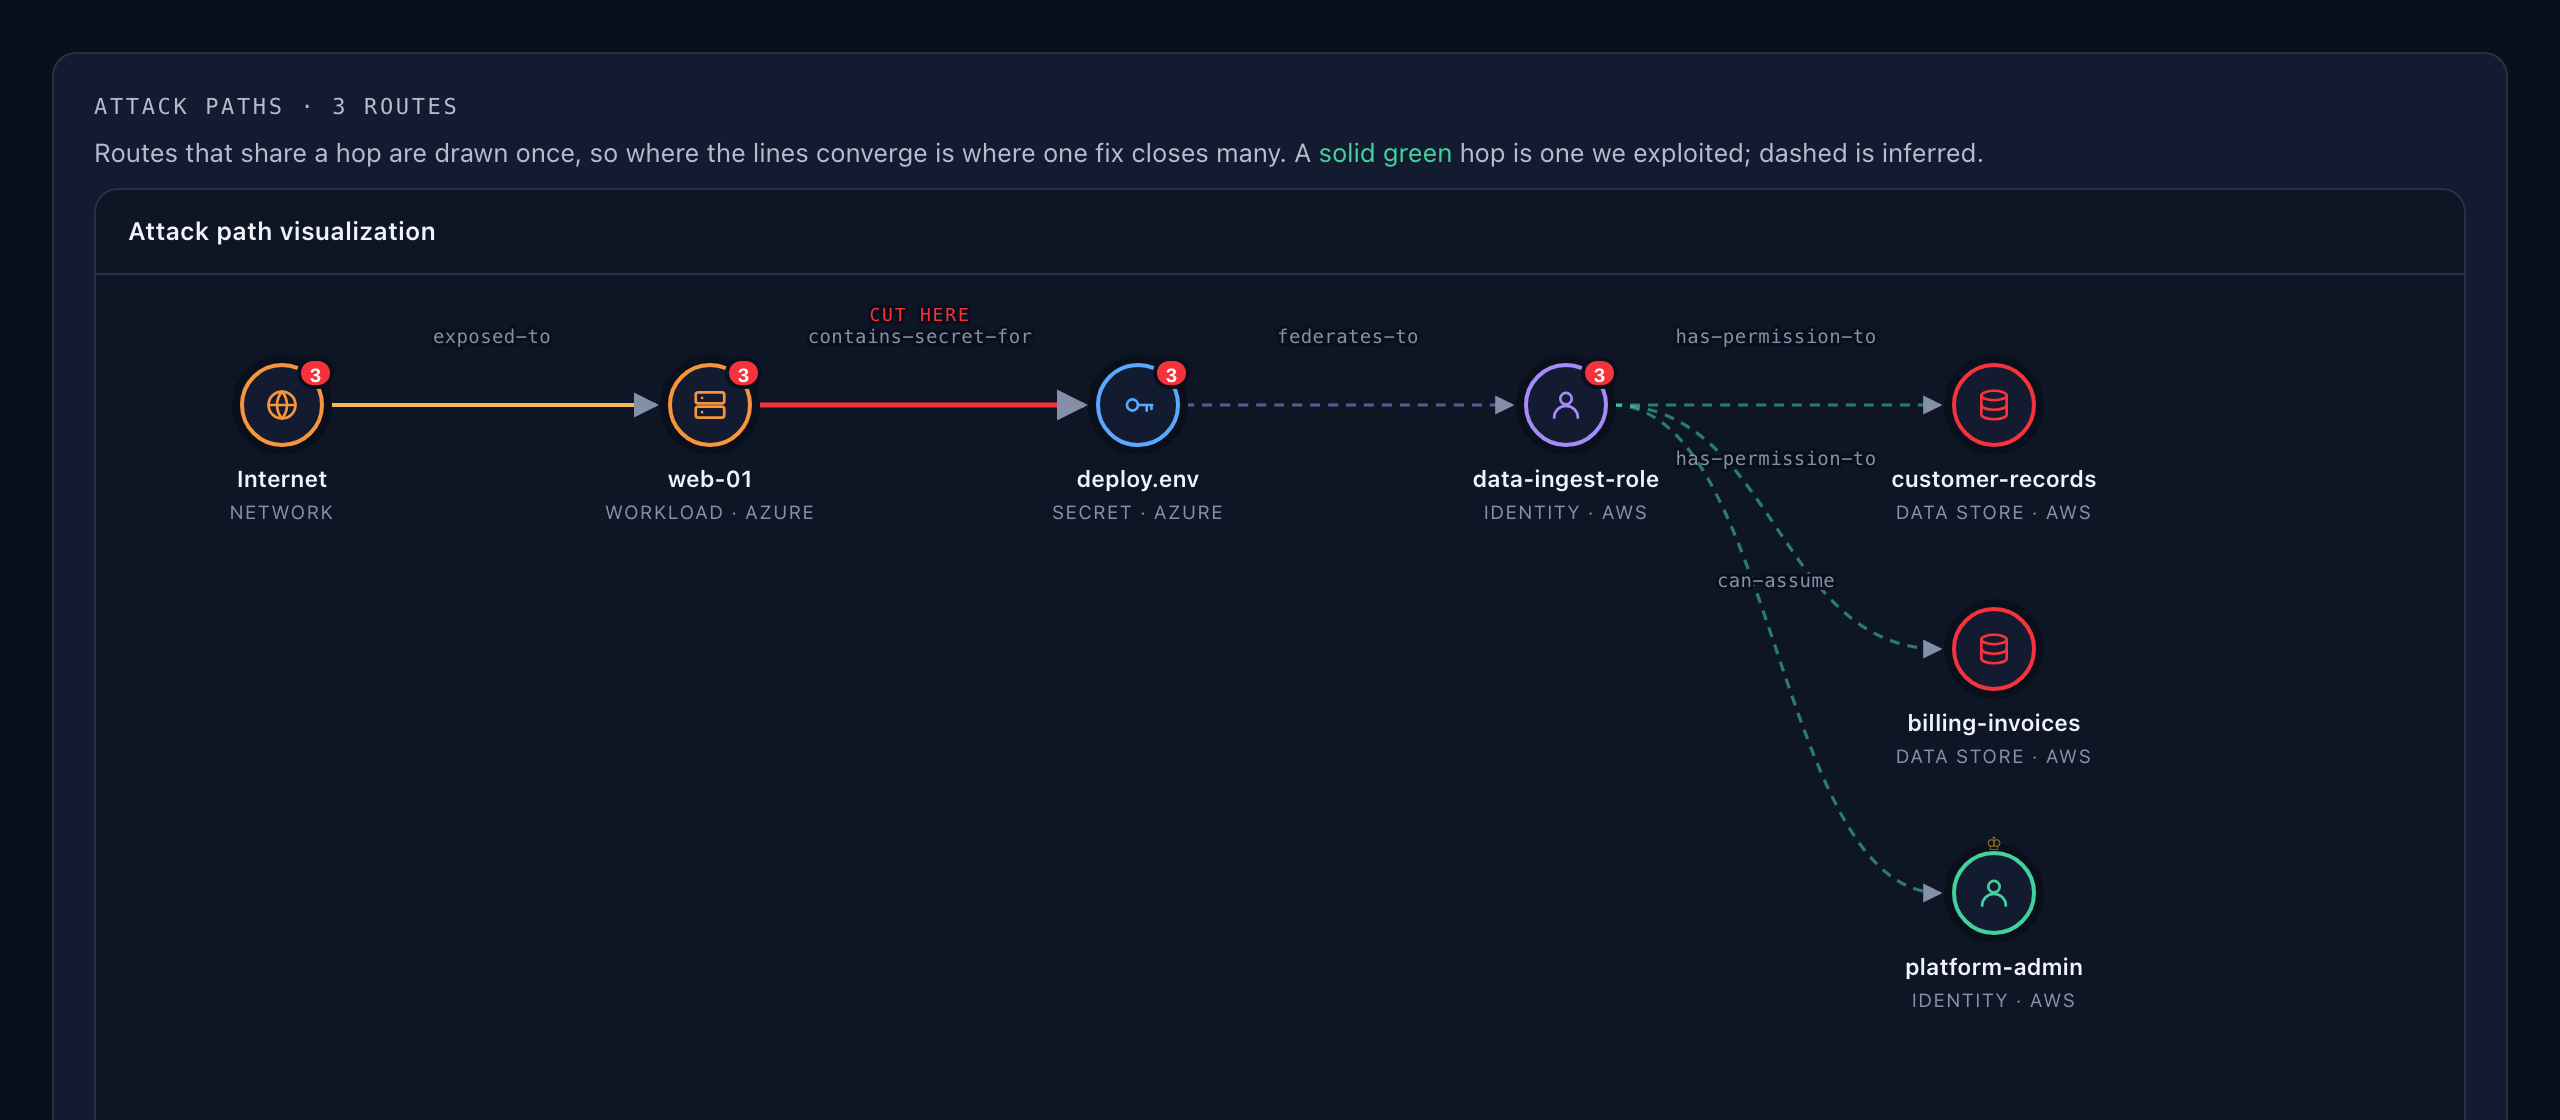
Redthread graph showing a ranked attack path across code, cloud and agents
How an assessment runs
01 · Connect
Read-only, in a few clicks
GitHub sign-in, your website URLs, and one-click cloud access for AWS, Azure, Google Cloud or Oracle. Connect one surface or all of them.
02 · Assess
Ranked by what's reachable
Every AI asset in one inventory, every risk placed on the graph, and the toxic combinations ranked first — each with the evidence for why.
03 · Act
Fix, prove, then control
Merge the fix, validate the critical paths with a working test, and give the agents you keep an identity and a policy.
What makes it different

One loop, not four products.

The scan that finds your agent also gives it an identity.
Discovery, identity and policy come from the same inventory, so nothing you decide to keep is ever unaccounted for — the gap behind OWASP's agentic risks for identity abuse, supply chain and rogue agents.
From a model key in Git to the data it can reach — closed by a pull request.
The path runs through code, the agent's cloud role and its way out to the internet. The assessment finds it end to end, and the fix lands where your engineers already work.
Cloud-neutral, and free to start.
AWS, Azure, Google Cloud and Oracle alike — not a feature of one cloud's console. The assessment is free with no sales call; the platform is priced on the size of your estate, not how often you scan.
Built for teams that ship every day

When development moves faster than security can map it.

CIOs and CISOs
An answer to "what AI are we running, and what could go wrong?" in plain language, with the evidence behind it.
Platform and security engineers
One graph instead of five consoles, an API to send findings to the tools you already run, and fixes as pull requests.
Investors and their portfolios
A consistent AI risk baseline across every company you back, with each company's data kept in its own workspace.

Find out what you're really running.

The complete assessment is free. Connect what you can — every surface you add makes the picture sharper.

Start a free assessment Book a demo