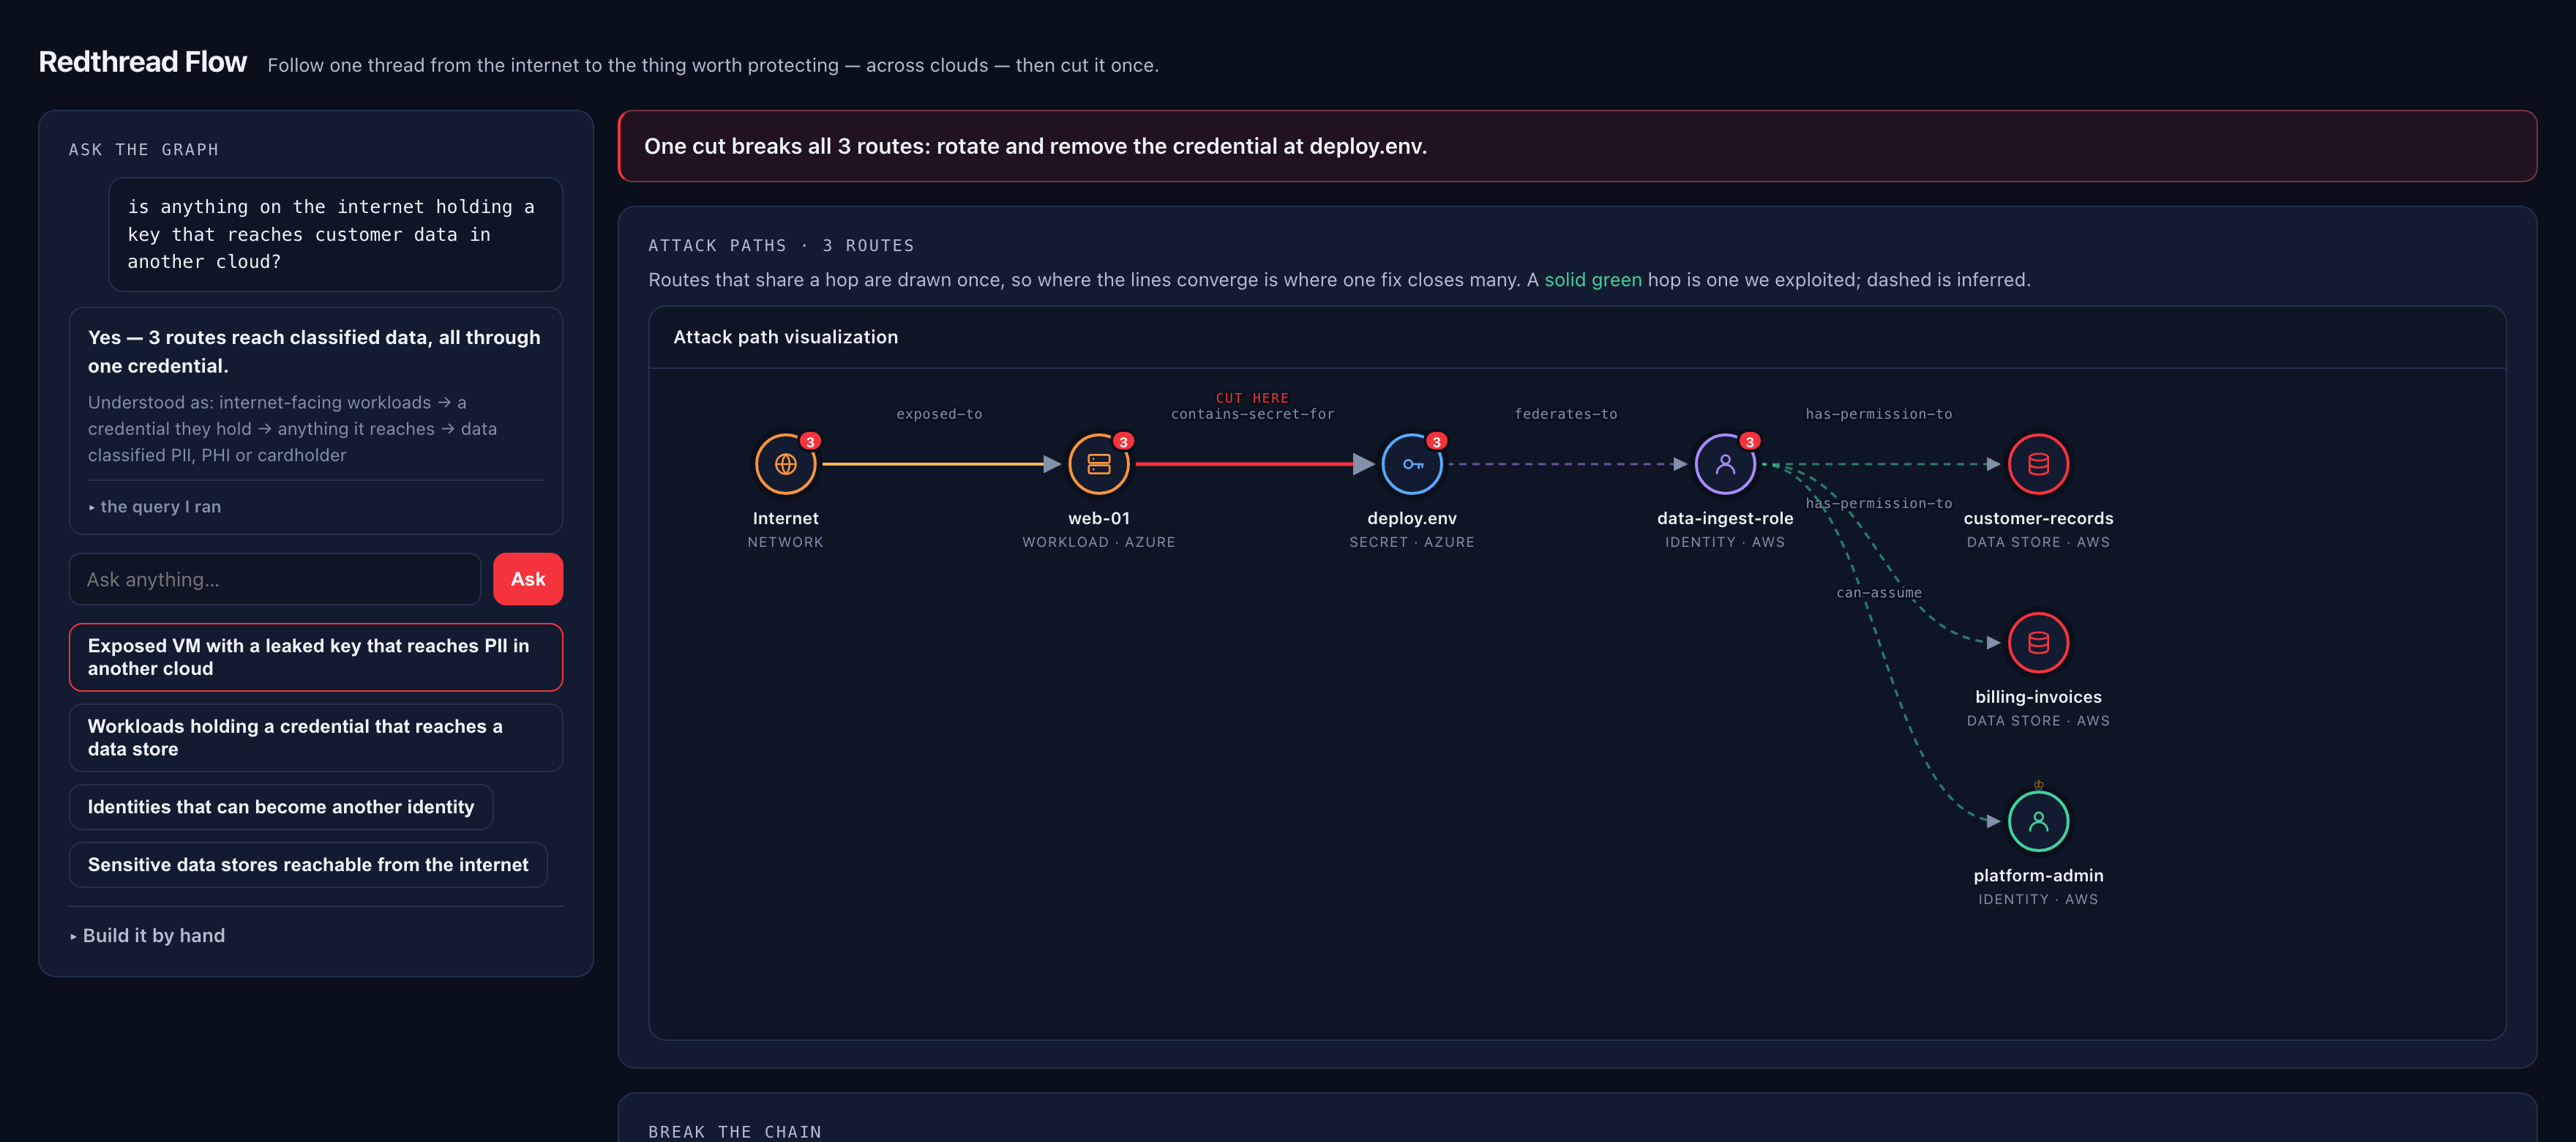
Product screenshot — Redthread Flow
Why the shift changes everything
01 — The shift

The agentic shift is here.

It's not coming — it's already realized. Every team now builds with AI: agents write the code, wire the infrastructure, and ship to production in hours. The way software gets made changed, and it changed for everyone at once.

02 — New surface

The attack surface exploded.

Every agent, prompt, tool and credential is a new way in — and the estate rewrites itself faster than any human can map.

03 — The gap

Old security can't keep up.

Config scanners hand you a list of what might be wrong. They never prove what an attacker can actually reach — so the path that spans layers slips by.

04 — Our solution

Our Solution.

MILLENNIUMS.AI is an AI-native security platform. At the core is a graph engine, Redthread, that maps and inventories your organization's entire AI infrastructure — every agent, tool, model, and data connection, including the shadow AI most teams don't know they're running. Then gives every agent in that graph a durable, cryptographically verified identity with our Agent Trust Fabric model.

01 / 04
Powered by Redthread

Total security at AI speed, powered by Redthread.

Redthread connects code, cloud, and runtime into a unified context graph. Context enables teams to use AI to fix exploitable risks at the source, stop attacks in real time, and start secure from the IDE — automatically and accurately.

For the first time, defenders can move faster than attackers — without sacrificing precision or slowing innovation.

Agent Trust Fabric
Agentic identity + continuous trust signals, on SPIFFE.

Know which agents you can trust — in real time, not in last quarter's report.

From proof to protection: real-time trust signals for every agent in your environment.

Agent Trust Fabric is the next step: it gives every agent in that graph a durable, cryptographically verified identity — built on SPIFFE, the open industry standard for workload identity, not a proprietary lock-in — and turns Redthread's proof into a live signal. The moment an agent is proven exploitable, or a fix is verified, a signed trust-state event broadcasts to whatever is orchestrating your agents: green means verified safe, red means proven unsafe, right now. No new dashboard to babysit. No waiting for the next scan cycle.

verified safe proven unsafe

One toggle turns it on. No agent rewrites, no new infrastructure to run yourself.

Redthread

A new operating model for AI-era security

One context graph runs all three teams — from code to cloud to agent identity to defend. Red proves it, Green prevents it, Blue stops it.

From first commit to continuous coverage: one agentic security lifecycle.

It starts with the graph. Everything that follows reads from it, writes back to it, and hands its context to the next step.

01
Graph
Connect agentless — every agent, repo, workload, identity, route and data store in one picture
02
Pentest
standard · deep · complete — no finding without a reproducible PoC
Live
03
Shadow-AI discovery
Candidates with an honest coverage banner — confirm to register
Repos live
04
Data security posture
What sits in your stores, through the same agentless role
Operator-enabled
05
Cloud and infra scanning
CVSS-scored checks across compute, storage, identity, network, K8s
Operator-enabled
06
Cross-cloud risk analysis
Federated trust between AWS, Entra ID and GCP
Operator-enabled
07
Realtime monitoring
An optional eBPF sensor beside your GuardDuty, Defender and SCC findings
Enterprise · detection only
Availability The graph, pentest and repo discovery are live and self-serve. Cloud and external enumeration, and the network, cloud and detection scan types, are enabled per tenant. The eBPF runtime sensor is an Enterprise add-on that detects and never blocks.
Then, on every change

Four things the graph makes possible.

Each of these reads the same estate the steps above built — which is why a change can be judged against what is already true in production.

01 New features deployment test
Test the release that changed, not the whole app again:
  • A baseline per target — only what changed is re-covered
  • An unchanged commit short-circuits: no scan, no charge
  • Recon carryover reuses the learned architecture and endpoints
Live
02 Constrain agents
An AI agent is an identity with permissions, and most have more than anyone intended:
  • Excessive-agency and tool-abuse testing
  • What the agent’s identity can actually reach, through the graph
  • The gap between scoped and reachable is what you constrain
Live
03 Code fix
A finding becomes a change your engineers review, never one we merge:
  • A minimal patch as a draft pull request on your own repo
  • Located by the identifiers the finding names — vendored and minified files excluded
  • Dependency updates proposed per CVE, with VEX decisions exported
Live
04 Prevention and response
The cheapest moment to stop a risk is before it exists:
  • The PR gate fails a change that would introduce an attack path
  • The GitHub Action gates the build — fail-on critical, high, medium, low, or never
  • A ticket in Jira or ServiceNow with the full path attached
PR gate live · runtime response roadmap
Where this does not go
Millenniums is a testing tool for staging and source, not a production runtime firewall. The optional eBPF sensor detects and never blocks, kills or quarantines. Real-time endpoint prevention (isolate a host, kill a process, quarantine a file) runs through a connected partner engine — the integration is live, and it activates the moment a partner is connected to your workspace. Admission control and cloud guardrails remain on the roadmap.